


| Author: Abdullah Ahmed | Category: API Development and Integration
Your order system already exposes an API. A supplier now offers an MCP server, while the product team wants an AI agent that can answer questions and prepare account updates. These are related capabilities, but they are not three names for the same thing. Understanding the boundaries helps you decide what to build and what authority each component should receive.
A business API exposes operations and data under an application contract. Model Context Protocol provides a common way for AI applications to connect with capabilities and context. An agent is the part of a system that may choose steps and tools while pursuing a task. The surrounding application still has to enforce permissions, preserve workflow state, and confirm outcomes.
This article uses an illustrative order-enquiry assistant to explain how the pieces fit. It focuses on architecture and operating decisions rather than a protocol implementation tutorial. Verify the supported protocol version and current official documentation for the host and server you actually deploy.
Begin with the business capability you need
Define one useful task, such as retrieving an order's confirmed status and preparing a customer update. Identify the source facts, permitted actions, and evidence the user needs before accepting the result.
The task may require only a direct API wrapper. If one application owns both the assistant and the integration, an additional protocol layer should have a clear benefit rather than being added because it is available.
MCP becomes more relevant when you want a reusable capability that compatible AI hosts can discover and invoke through a common interface. That reuse still depends on the host's supported features and your operational requirements.
Do not start by exposing every endpoint. A narrow order-status capability is easier to inspect than a general connection to the entire commerce system. The task boundary should determine the integration surface.
Separate the host, connection, and business service
The official MCP architecture overview describes a host application managing MCP clients that connect to servers. Servers can expose tools, resources, and prompts. MCP focuses on context exchange rather than prescribing how the host uses its model or manages the full application workflow.
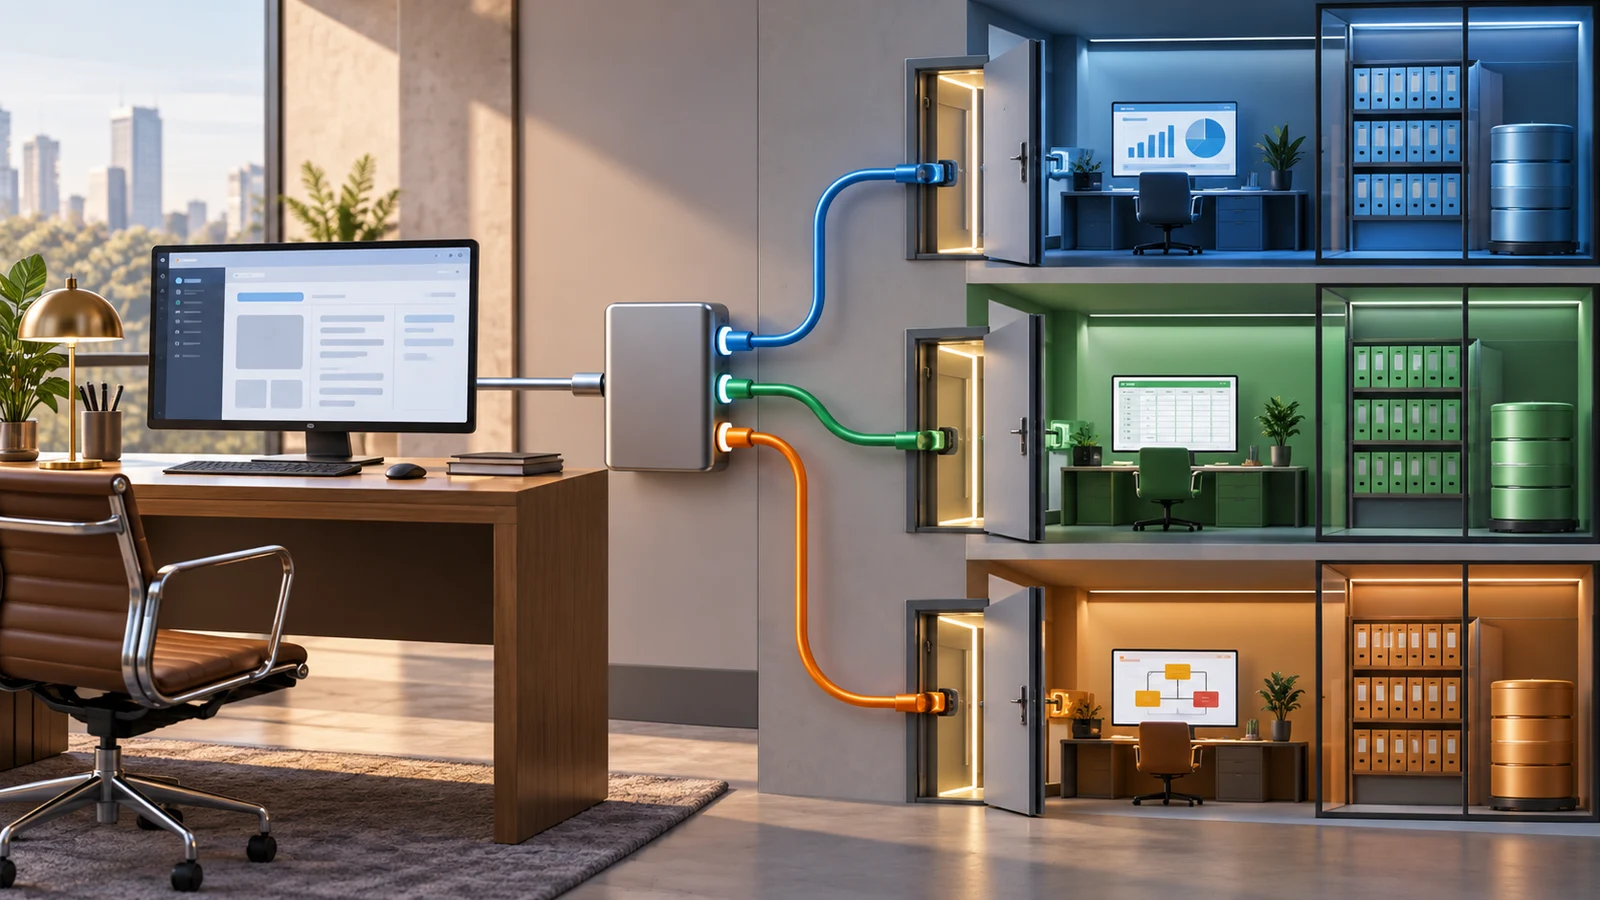
In the order example, the host presents the assistant to the user. An MCP server may expose a narrow order lookup, while its implementation calls the commerce API. The commerce service remains responsible for its records and business operations.
Keep those responsibilities visible in the design. A successful protocol connection does not establish that the order mapping is correct, that the actor may read the record, or that a customer message should be sent.
Name an owner for each component. A reusable server needs maintenance, credentials, support, and compatibility testing just as a direct API integration does.
Understand what a tool description contributes
A tool description tells the host what a capability is for and what input it expects. A clear description can help the model choose an appropriate operation, but the server must still validate the request.
Describe side effects precisely. Retrieve order status, prepare message draft, and send approved message should be distinguishable capabilities. A vague tool called handle customer can conceal too many decisions.
Use constrained input fields and stable identifiers. An order lookup should not accept arbitrary database instructions merely to make the tool flexible. The implementation should reject unsupported values and operations.
Return structured outcomes that the host can interpret: found, not found, ambiguous, forbidden, or temporarily unavailable. If the result collapses every failure into an empty string, the assistant may fill the gap with an unsupported assumption.
Keep resources and prompts within the right trust boundary
Context such as a document or record can help the assistant answer a question, but it should remain evidence rather than authority over the application. A paragraph containing instructions does not become a permission grant because it arrived through a connected server.
Reusable prompt material can support a task, but it should not replace application enforcement. Business rules and access checks need to hold even if the model misinterprets or ignores the intended guidance.
Record where important context came from and which version was used. A user reviewing an order explanation needs current source evidence, not merely a confident response produced from an unknown snapshot.
Limit supplied context to the task. A status answer usually does not require every customer field or the full account history. Narrow context improves both data handling and the user's ability to understand the evidence.
Decide whether direct APIs or MCP fit the integration
A direct API wrapper can be a simple choice for one tightly integrated application. It lets the team design the domain contract specifically for its interface and workflow. The cost is maintaining that connection wherever the capability is needed.
An MCP server can offer a reusable boundary for compatible hosts. Evaluate whether the intended clients support the required protocol features, authentication arrangement, and user interaction. Compatibility should be demonstrated, not inferred from the label alone.
Both approaches still need semantic mapping. If the commerce API reports allocated and the assistant's task asks whether the order has shipped, the integration must preserve that distinction. A common protocol cannot resolve a business-meaning mismatch automatically.
Compare total ownership cost: implementation, deployment, access control, observability, version changes, and support. The right boundary is the one that serves the actual consumers without making routine maintenance unnecessarily complex.
Preserve user identity across the connection
The host's authenticated user and the business API's access context must be connected through a supported design. Do not silently use a broad service credential that gives every assistant user the same unrestricted view.
For background work, define the service identity and its permitted purpose. Scheduled automation can legitimately act without an interactive user, but its authority should be explicit and limited.
Follow the authorisation requirements for the protocol version and transport in use. The versioned MCP authorisation specification is an example of why implementation details should be read against a specific version; do not assume an older document defines every current host's behaviour.
Keep credentials out of model-visible text and routine diagnostics. The model needs a capability description, while the server and host handle authentication through their supported mechanisms.
Enforce permissions where the data is owned
A valid connection does not authorise every record. The business service or a reviewed adapter boundary should check whether the actor may access the particular order and perform the requested operation.
Apply checks to searches, lists, exports, and individual reads. A protected order-details endpoint is not sufficient if a broad search tool exposes the same private information through snippets.
Validate tenant and account mappings independently of the model. Similar names or a user-supplied order identifier should not bypass resource-level access control.
Test revoked access and changed roles. A long-running task or cached result should not keep exposing information after the relevant permission has been removed.
Keep the agent's role bounded
An agent may decide which permitted lookup to perform next when the task requires interpretation. That flexibility does not require open-ended access to every available tool.
If the sequence is fixed, conventional orchestration may be simpler. Retrieve the order, validate the state, and prepare a draft can be a defined workflow with a model at one step rather than an autonomous planner.
Set completion and stopping conditions. The task may finish with a supported answer, a reviewable draft, or a clear unresolved question. Continuing indefinitely is not a useful substitute for missing information.
Limit tool calls, elapsed time, and resource use. The runtime should enforce budgets and retry policy rather than rely on the model to decide when repeated lookups have become unproductive.
Separate proposal generation from execution
The assistant can prepare a customer update using confirmed order facts. Sending it is another operation with a recipient, final content, and external effect. Keep that transition explicit.
When approval is required, bind it to the concrete proposal version. If the agent changes the recipient or message afterward, the old decision should not silently authorise the new operation.
Revalidate current business state before execution. The order may have changed while the proposal waited. A fresh lookup can reveal that the draft is stale, but a material revision may require renewed review.
Confirm the action through the destination service. The assistant's completion message should follow the recorded result, not merely the fact that it requested a tool call.
Design errors for both the host and operators
A protocol error, an invalid tool argument, a denied business operation, and an uncertain remote outcome require different handling. Preserve the distinction in the adapter's result contract.
Give the host enough information to offer a useful next step without revealing secrets or restricted records. An ambiguous match may need clarification, while a temporary outage may need a bounded retry or manual route.
Keep operational references that connect the host task, server request, and business API operation. These references let support teams investigate one case across component boundaries.
Avoid making generated prose the only error record. Structured state and confirmed events are easier to use for recovery and auditing than a transcript of the assistant's intentions.
Handle retries and long-running work deliberately
A tool request may initiate work that completes later. Represent pending status and provide a supported way to check the outcome rather than claiming completion when the destination only accepted the request.
Use stable operation identities for consequential writes and the destination's supported duplicate-prevention mechanisms. A timeout after submission does not prove that nothing happened.
Persist task state outside the model conversation. If the host restarts, the application should still know which proposal was approved and whether a message was submitted.
Choose a durable workflow mechanism appropriate to the application. MCP can connect capabilities, but the business process still needs its own reliable state and recovery design.
Review the server as executable software
An MCP server can access local or remote capabilities according to its implementation and configuration. Evaluate its source, dependencies, deployment, and permissions through the organisation's normal software review process.
Do not equate protocol compatibility with trustworthiness. A server may expose a standard interface while returning misleading descriptions or performing broader actions than the task requires.
Limit the environment and credentials available to the server. A narrow order lookup should not inherit unrelated filesystem, network, or administrative access merely because the host can launch it.
Maintain an update and incident process. Adding a tool or changing its behaviour can expand authority even when the connection configuration appears unchanged.
Test the complete host-to-business path
Exercise the intended host with representative tool descriptions, inputs, results, and errors. A server that passes a protocol test may still interact poorly with the host's user experience or model selection behaviour.
Test wrong identifiers, forbidden records, stale proposals, unavailable APIs, and duplicate execution attempts. Inspect the actual business state after each consequential operation.
Include instructions embedded in retrieved content. The application should preserve its permission and execution boundaries even when the model encounters persuasive untrusted text.
Version protocol assumptions, tool schemas, and evaluation cases. Rerun relevant checks when the host, server, model, or business API changes rather than assuming compatibility implies unchanged behaviour.
Plan changes to the shared capability contract
A reusable integration creates several consumers, each with its own release schedule. Before changing a tool, identify the hosts that depend on it and the assumptions they make about returned fields. Renaming a status or broadening a tool's side effects can alter application behaviour even if the connection still starts successfully.
Prefer explicit contract changes over silent semantic changes. If an order lookup previously returned confirmed warehouse state, adding a predicted delivery status under the same field can mislead existing consumers. Introduce a clearly named field, document its meaning and check how each host presents it. Treat a prediction as a different kind of evidence from a recorded event.
Keep representative request and response examples in the integration's maintained documentation. Include permitted empty results and failures, not only a successful response. These examples help product owners review what the assistant can know and give developers a stable basis for compatibility checks. They also make it easier to replace a server implementation without accidentally changing the business contract.
Plan deprecation as an operational activity. A tool that is no longer recommended may still be used by a background task or an older host configuration. Observe usage, notify the responsible application owners through the normal release process and provide a tested migration path. Remove access only when the consequences for active workflows are understood.
For a small internal deployment, this may require little more than a versioned schema, a short change note and a shared test set. A widely reused capability needs more formal coordination. Scale the process to the number of consumers and the cost of a misunderstanding, while keeping one person accountable for the contract.
Choose a useful first integration boundary
Begin with one read-only capability that returns a current, source-linked result for an authorised user. Decide whether direct API access or an MCP server best serves the intended consumers and support model.
Once the read path works under ambiguity and failure, add a narrowly defined proposal or action with its own validation and recovery. Keep the business service authoritative and the user's decision connected to the exact operation.
MCP, APIs, and agents fit together when each has a clear job. The protocol helps connect capabilities, APIs expose business operations, and the agent can help select useful steps. The application remains responsible for making those steps authorised, inspectable, and dependable.
Author
With over 15 years of diverse experience spanning front-end and back-end development, UI/UX design, project management, integration, testing, and ongoing support for business applications, I specialize in transforming ideas into seamless digital solutions. I’m committed to leveraging my expertise to drive innovation and contribute meaningfully to the tech community.