


| Author: Abdullah Ahmed | Category: API Development and Integration
The existing application already has users, permissions, records, and a release process. A team adds a language-model API call to summarise case notes, and the demonstration works. The production questions arrive immediately: which records may be sent, what happens when the provider is slow, how is an incomplete response handled, and can the feature be turned off without disrupting the case-management system?
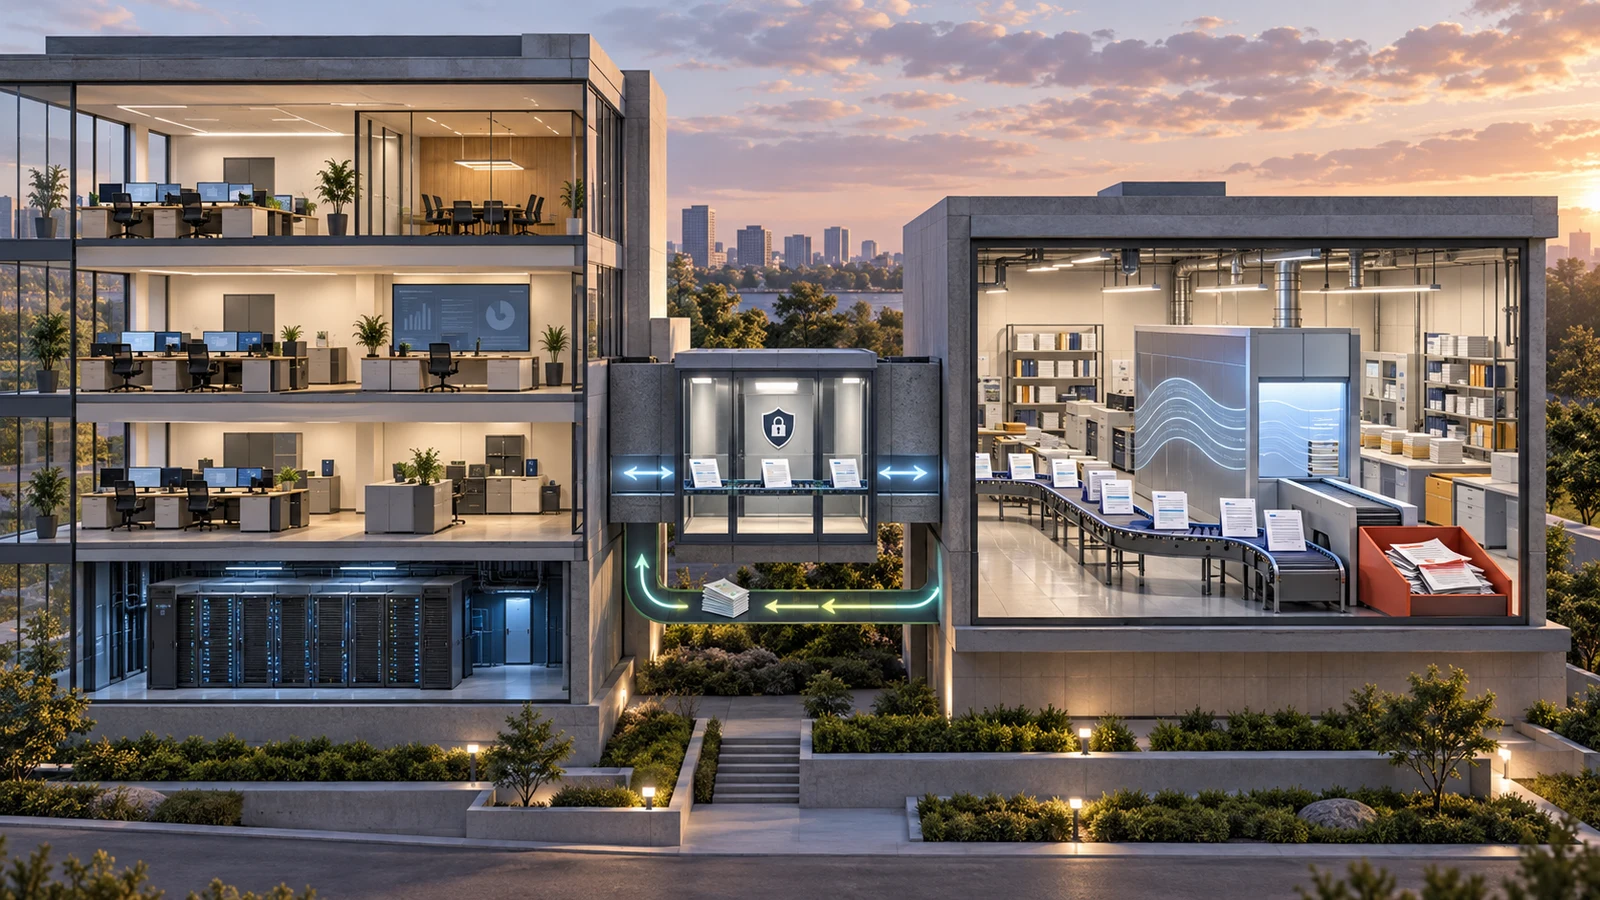
Integrating a large language model is an application-design task, not merely an HTTP request. The model service supplies a capability with its own contract and failure modes. Your software must decide how that capability fits the business workflow and how users can inspect its output.
This guide follows a case-summary feature inside an established business application. It focuses on provider-independent design choices so the team can implement against the selected API's current documentation without making the rest of the product depend on one response shape or optimistic demonstration.
Choose a narrow first capability
Define what the feature should produce and who will use it. A case summary might identify confirmed events, unresolved questions, and source references for an employee preparing a handoff. It should not silently update the authoritative case facts.
Specify the input scope. The feature may use selected notes and related records that the current user is permitted to access. A broad instruction to summarise everything can hide both access and relevance problems.
Write acceptance criteria in terms of the task. The summary should preserve important dates, distinguish facts from interpretation, and identify missing information. Its value should be measured through handoff preparation and review effort, not only writing quality.
Avoid combining several new capabilities in the first release. Summarisation, automatic routing, message sending, and record updates have different requirements. A narrow read-and-draft feature provides useful evidence before execution authority expands.
Put the provider behind an application adapter
Create a maintained boundary between the business application and the model API. The rest of the system should request a domain capability, such as prepare case summary, rather than constructing provider-specific payloads in every controller.
The adapter can own authentication, request construction, response parsing, timeouts, and error translation. Keep domain validation and permissions in the appropriate application services rather than hiding all behaviour inside a generic client wrapper.
Return an application-level result with clear states: completed draft, insufficient input, temporarily unavailable, or invalid output. This lets the interface respond consistently even when provider errors differ.
Avoid promising effortless provider switching. Different models and APIs can behave differently even behind the same interface. The adapter reduces coupling, while evaluation establishes whether an alternative is suitable for the task.
Review the API contract before implementation
Confirm supported authentication, request limits, response formats, timeout behaviour, rate-limit handling, and available asynchronous or streaming modes. Use the provider's current official documentation for the exact implementation.
Check the service's data-handling and retention options against the organisation's requirements. Do not infer them from a product name or from the behaviour of a different service offered by the same vendor.
Identify which features are necessary. A constrained summary may not need tools, conversation persistence, or a complex agent framework. Reducing the required surface makes integration and testing easier.
Record relevant assumptions in the adapter documentation. If the implementation depends on a specific output feature or API version, future maintainers should be able to identify that dependency before upgrading.
Enforce access before assembling context
The application should verify which source records the actor may use before building the model request. Do not retrieve a broad dataset and ask the model to hide restricted details afterward.
Apply resource-level checks to related records and attachments, not only the main case. A user allowed to view a case may still lack access to a confidential note or a separate account's information.
Send the minimum useful context. Exclude credentials, unnecessary personal details, and irrelevant history. Smaller, relevant inputs can also improve reviewability because users can understand what the summary considered.
Preserve source identifiers outside the generated prose. The application should know which records and versions were included even if the model omits a reference or produces an invalid answer.
Assemble evidence deliberately
Long case histories may require selecting relevant records or using retrieval. Define what relevance means for the task: recent events, unresolved commitments, or a specified date range. Do not let an arbitrary truncation silently determine the summary's scope.
If some material is excluded, make that boundary available to the user where it affects interpretation. A summary of the latest ten notes should not be presented as a complete account history.
Use stable source references and retain their mapping to the request. The model can return references to those identifiers, and the application can validate that they correspond to material actually supplied.
Test cases where sources conflict. The desired output may identify the disagreement rather than choose one value. A summary should not erase uncertainty that a handoff recipient needs to understand.
Require structure, then validate meaning
A structured response can make the feature easier to display and test. Define fields such as summary points, unresolved questions, and source references. Use the provider's supported structured-output facilities if they fit the task.
Schema compliance is only the first check. A valid date field can contain the wrong date, and a valid source identifier can be attached to an unsupported claim. Evaluate semantic correctness separately.
Validate references, lengths, required fields, and allowed states in application code. Handle malformed or incomplete output through a clear failure path rather than trying to render arbitrary content as trusted markup.
Keep the model result as a draft unless the workflow explicitly authorises another use. A valid summary should not become an automatic source of truth for case status or customer commitments.
Design the user experience around asynchronous work
A model request may take longer than a familiar form action. Decide whether the user should wait interactively or receive a background task that can be revisited. The choice depends on the task and latency budget.
Show that work has started and preserve the user's input. If the user leaves the page, the system should behave predictably: cancel if supported, continue as a background job, or explain the required interaction model.
Use progress information derived from actual application events. A generated sentence saying the system is checking records is not proof that a lookup occurred. Avoid presenting invented progress as an operational fact.
Provide a useful unavailable state. Employees should still be able to read the original notes and complete essential work when summarisation fails. The fallback should be part of the interface rather than hidden in a help page.
Set timeouts and retries at the right boundary
Define how long an interactive request may wait and how long a background job may run. An unbounded call can tie up resources and leave users uncertain about whether the system is working.
Retry transient failures within a bounded policy, taking account of provider guidance and rate limits. Do not retry every error: invalid input, denied access, and unsupported output may require different handling.
Repeated generation may produce different text and additional cost. Record attempts and decide whether a new result replaces or accompanies an existing draft. Do not silently overwrite a version the user has already reviewed.
If the feature later includes external actions, separate generation retries from action retries. Recreating a summary and resending a customer message have very different consequences. Persist operation identities for consequential writes.
Keep prompts and business rules in distinct roles
The prompt should describe the interpretation task, output expectations, and relevant boundaries. The application should enforce permissions, allowed operations, and business state transitions independently.
Version prompts alongside the capability's implementation or configuration. Review changes with examples that show their intended effect. A small wording change can alter omission, tone, or reference behaviour.
Do not embed secrets or credentials in prompts. The model does not need them to prepare a summary. Authentication belongs in the integration service and should be excluded from diagnostic output.
Treat source text as data even when it contains imperative language. A customer note that tells the assistant to ignore instructions should remain content to analyse, not a new authority over the application.
Apply security controls to the complete data path
Review input assembly, external transmission, response parsing, rendering, storage, and logging. A safe API credential does not protect against every failure elsewhere in the workflow.
Sanitise or escape output according to the display context. Generated text should not bypass the protections used for other untrusted content. Validate links and active markup if the feature permits them.
OWASP's prompt-injection prevention guidance discusses the difficulty of keeping instructions separate from untrusted content in language-model systems. Use defence in depth: constrained access, validation, careful context handling, and monitored execution rather than a single protective sentence in the prompt.
Limit diagnostic retention to what the organisation needs. Request identifiers, configuration versions, durations, and error categories may be sufficient for many investigations without retaining every source record and generated token.
Establish a representative evaluation set
Use real-shaped cases with appropriate data handling: short notes, long histories, repeated events, conflicting dates, missing context, and content that should remain unresolved. Have domain users define the expected qualities of a useful summary.
Measure factual preservation, unsupported additions, missed commitments, reference correctness, and review effort. A single overall score can hide a failure that matters to handoff quality.
Keep some cases separate from prompt development. Repeatedly optimising around the same examples can create an unrealistic impression of quality. Add newly discovered failure types to the evaluation process deliberately.
Run the set when changing the model, prompt, retrieval logic, source selection, or response schema. Treat those changes as product changes even when the frontend remains identical.
Observe cost and performance by completed task
Track request duration, failures, retries, input size, output size, and provider usage under the selected billing model. Connect those measures to an accepted summary or completed user task.
Include review and support effort in the operating picture. A low-cost model response can still be expensive if employees must repeatedly check and repair it. The relevant denominator is useful completed work.
Use limits on input length, output size, concurrency, and repeated attempts appropriate to the application. Avoid truncating important evidence silently just to remain within a technical limit.
Plan for bursts and shared provider quotas. Several features may use the same service account or rate limit. Central coordination can prevent one background job from making an interactive feature unavailable.
Release behind a controlled capability boundary
Enable the feature for a small eligible group or case type first. Keep a switch that stops new model work while preserving normal application access and any already saved drafts.
Compare the assisted workflow with the existing method. Ask users to complete real handoffs and inspect where the summary helps, where it omits important information, and how much verification it requires.
Document support ownership, escalation, and provider incident handling. An external service dependency needs an operating plan even when the integration is small.
Avoid expanding from summarisation to automatic decisions without a new review of authority and recovery. The same model can support both, but the surrounding system requirements are materially different.
## Decide whether caching fits the evidence model
Caching can reduce repeated work when the same authorised input produces a reusable draft, but the cache key must reflect the source version and relevant task configuration. A summary of yesterday's case notes should not be returned as current after a new event is added.
Include permission boundaries in the design. A cached result prepared for a user with broader access must not be served to someone who cannot view its sources. Avoid treating a shared case identifier as sufficient proof that every actor may see the same summary.
Decide whether user edits are cached output or a separate reviewed draft. Regenerating the model result should not replace a human-edited version silently. Store those states distinctly.
Test invalidation with changed records, removed access, and configuration updates. Caching is an application feature with correctness requirements, not merely a performance switch.
Make stored outputs explainable later
If the application retains summaries, keep enough metadata to identify the source set, creation time, and capability version. This lets users distinguish a saved historical draft from a freshly generated view.
Provide a clear refresh action when current information is needed. Show material differences or preserve the earlier version where the workflow requires an audit.
Avoid storing every response indefinitely without a purpose. Define retention for drafts, accepted outputs, and diagnostic material separately, using the organisation's requirements.
These decisions make the feature easier to maintain because a reported problem can be connected to a specific request and evidence set instead of an unrepeatable impression of what the model once said.
Preserve long-term maintainability
Keep the provider adapter, domain validation, task state, and interface responsibilities clear. This gives future maintainers a place to change one part without rewriting the entire feature.
Record configuration versions with stored outputs when needed for investigation. A user reporting a poor summary should be traceable to the source set and capability version that produced it.
Plan for deprecation and replacement through evaluation rather than assumption. If a model or endpoint changes, test the task against the new option and update the contract where necessary.
The first milestone is a summary feature that fails clearly, respects access, preserves evidence, and helps users finish a handoff. Once that boundary is dependable, adding language-model capability becomes a maintained extension of the existing application rather than an isolated API call whose behaviour the business cannot explain.
Author
With over 15 years of diverse experience spanning front-end and back-end development, UI/UX design, project management, integration, testing, and ongoing support for business applications, I specialize in transforming ideas into seamless digital solutions. I’m committed to leveraging my expertise to drive innovation and contribute meaningfully to the tech community.